Run
Security Baseline & Hardening
Assess your attack surface, close the gaps, and build defence-in-depth security that hardens every layer — from network perimeter to application code.
You can't protect what you haven't measured.
Most organisations don't get breached because they lack tools — they get breached because they lack visibility. Default configurations, orphaned accounts, unpatched systems, and flat networks create an attack surface that grows silently. CBM starts with a rigorous baseline assessment, then systematically hardens every layer until your security posture is measurable, auditable, and continuously improving.
80%
Of breaches involve compromised or mismanaged credentials
197
Average days to identify a breach without continuous monitoring
60%
Of SMBs close within 6 months of a major cyber incident
What We Deliver
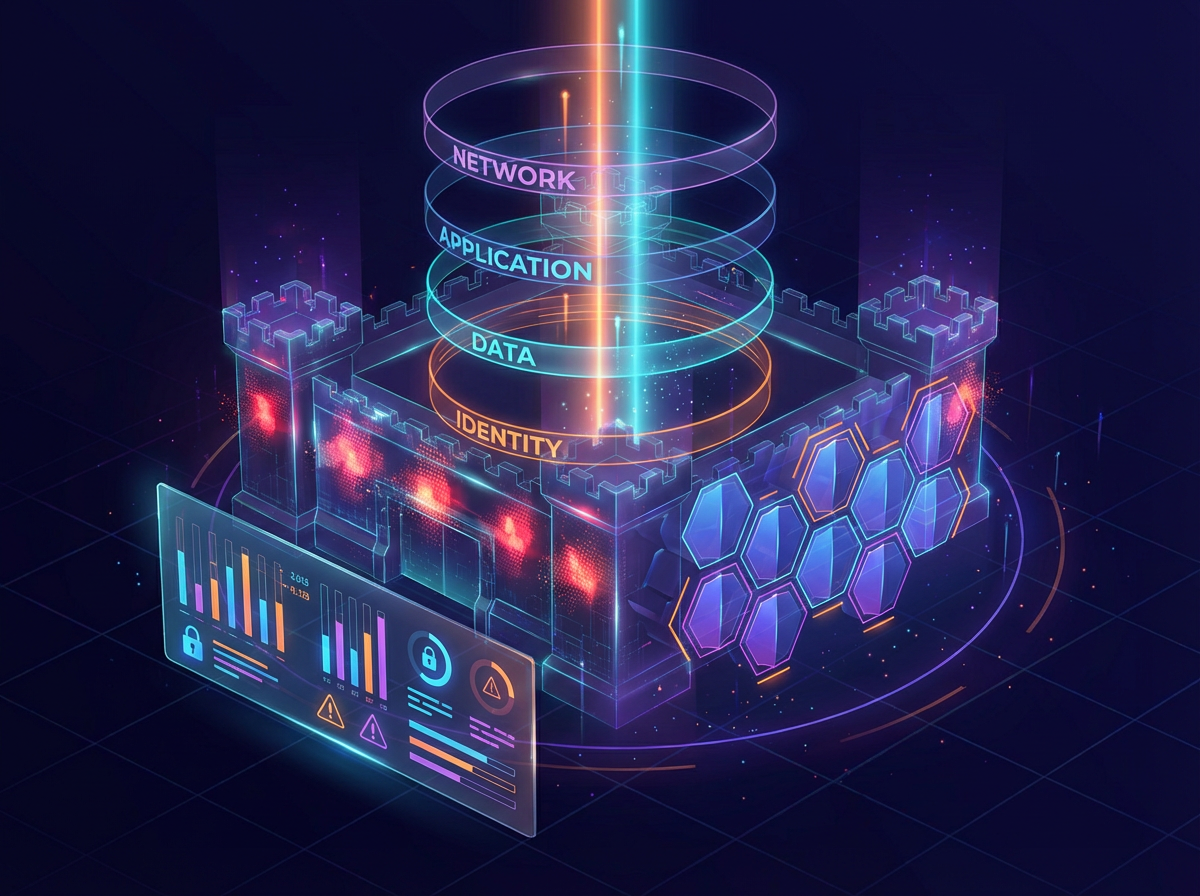
Defence-in-depth, not checkbox security
We harden every layer of your stack — infrastructure, identity, application, and data — with automated enforcement that keeps you secure between audits, not just during them.
Security Baseline Assessment
Comprehensive audit of your infrastructure, applications, and processes against CIS Benchmarks, NIST, and industry best practices — scored, prioritised, and actionable.
Infrastructure Hardening
OS-level lockdown, network segmentation, firewall tuning, and attack surface reduction across servers, containers, and cloud resources.
Identity & Access Management
Least-privilege enforcement, MFA rollout, privileged access management, and service-account hygiene — because 80% of breaches involve compromised credentials.
Compliance Frameworks
Map your security posture to ISO 27001, SOC 2, GDPR, PCI-DSS, and NIS2 — with automated evidence collection and continuous compliance monitoring.
Application Security
Code review, SAST/DAST integration, dependency scanning, and secure SDLC practices that catch vulnerabilities before they reach production.
Automated Remediation
Policy-as-code enforcement, auto-patching pipelines, and drift detection that fix misconfigurations before attackers find them.
How We Work
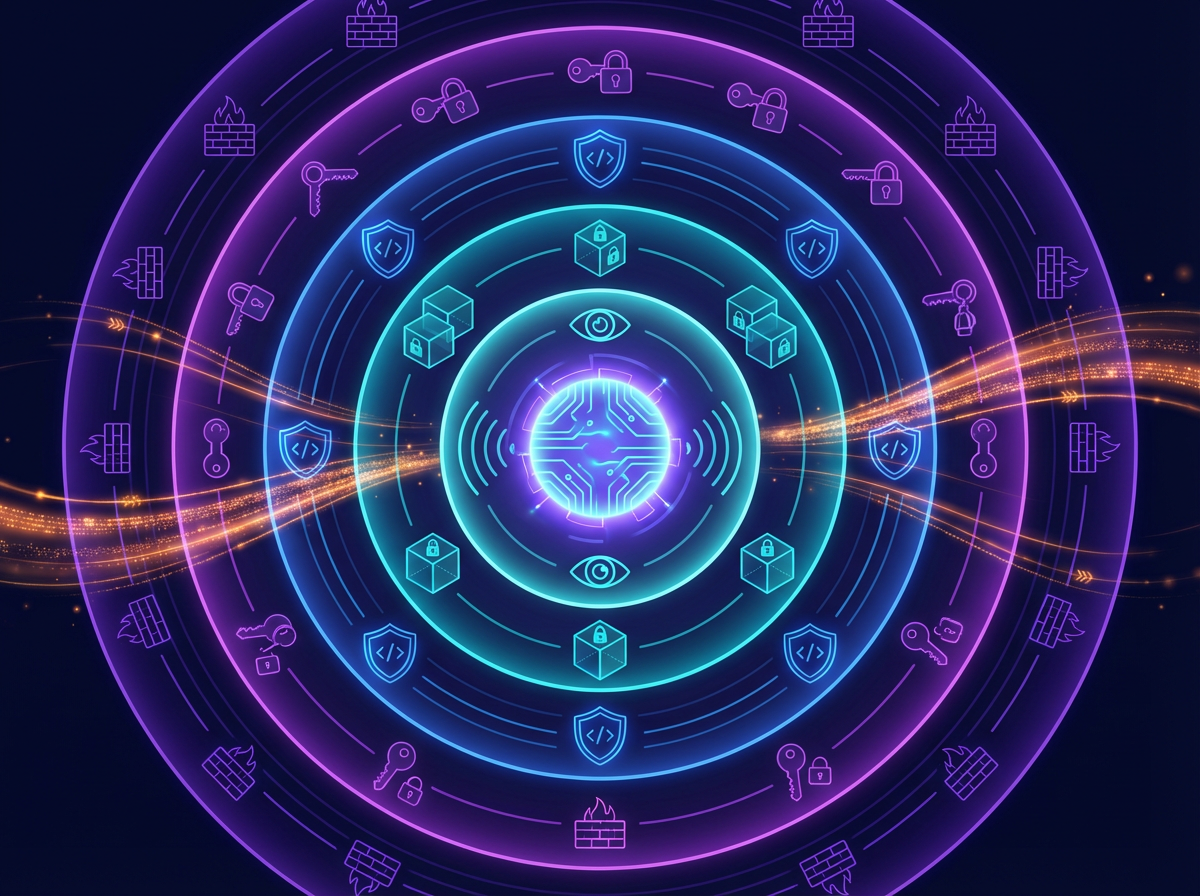
From assessment to continuous assurance
Discovery & Risk Assessment
We map your attack surface — assets, data flows, access patterns, and existing controls — and produce a risk-ranked vulnerability report.
Hardening Blueprint
Prioritised remediation plan: CIS benchmark alignment, network redesign, IAM overhaul, and compliance gap closure — all documented with effort estimates.
Implementation & Validation
Wave-by-wave hardening — infrastructure, identity, application, and data layers. Each wave is validated with penetration testing and compliance scans.
Continuous Assurance
Automated compliance monitoring, drift alerts, quarterly re-assessments, and incident response playbooks — security that improves over time, not just at audit time.
Technology
Enterprise-grade tooling. No vendor lock-in.
We combine best-of-breed security tools with open-source automation — tailored to your stack, your compliance requirements, and your budget.
Assessment
- Nessus
- Qualys
- OpenVAS
- CIS-CAT
IAM
- Okta
- Azure AD
- AWS IAM
- Vault
Network
- Palo Alto
- Cloudflare
- Cilium
- Calico
AppSec
- SonarQube
- Snyk
- Burp Suite
- OWASP ZAP
Compliance
- ISO 27001
- SOC 2
- GDPR
- PCI-DSS
Automation
- OPA
- Sentinel
- Falco
- Checkov
Ready to know where you stand — and close the gaps?
Tell us about your environment. We'll assess your security baseline, prioritise the risks, and give you a hardening roadmap — no obligations.